Blog
Practical guides to AI agent authorization.
Understand the controls. Review the evidence. Put an approval boundary around the actions that matter.
Start here
Where should a human approve an AI action?
A practical guide to choosing the boundary, holding the action and recording the decision.
Read the approval guide →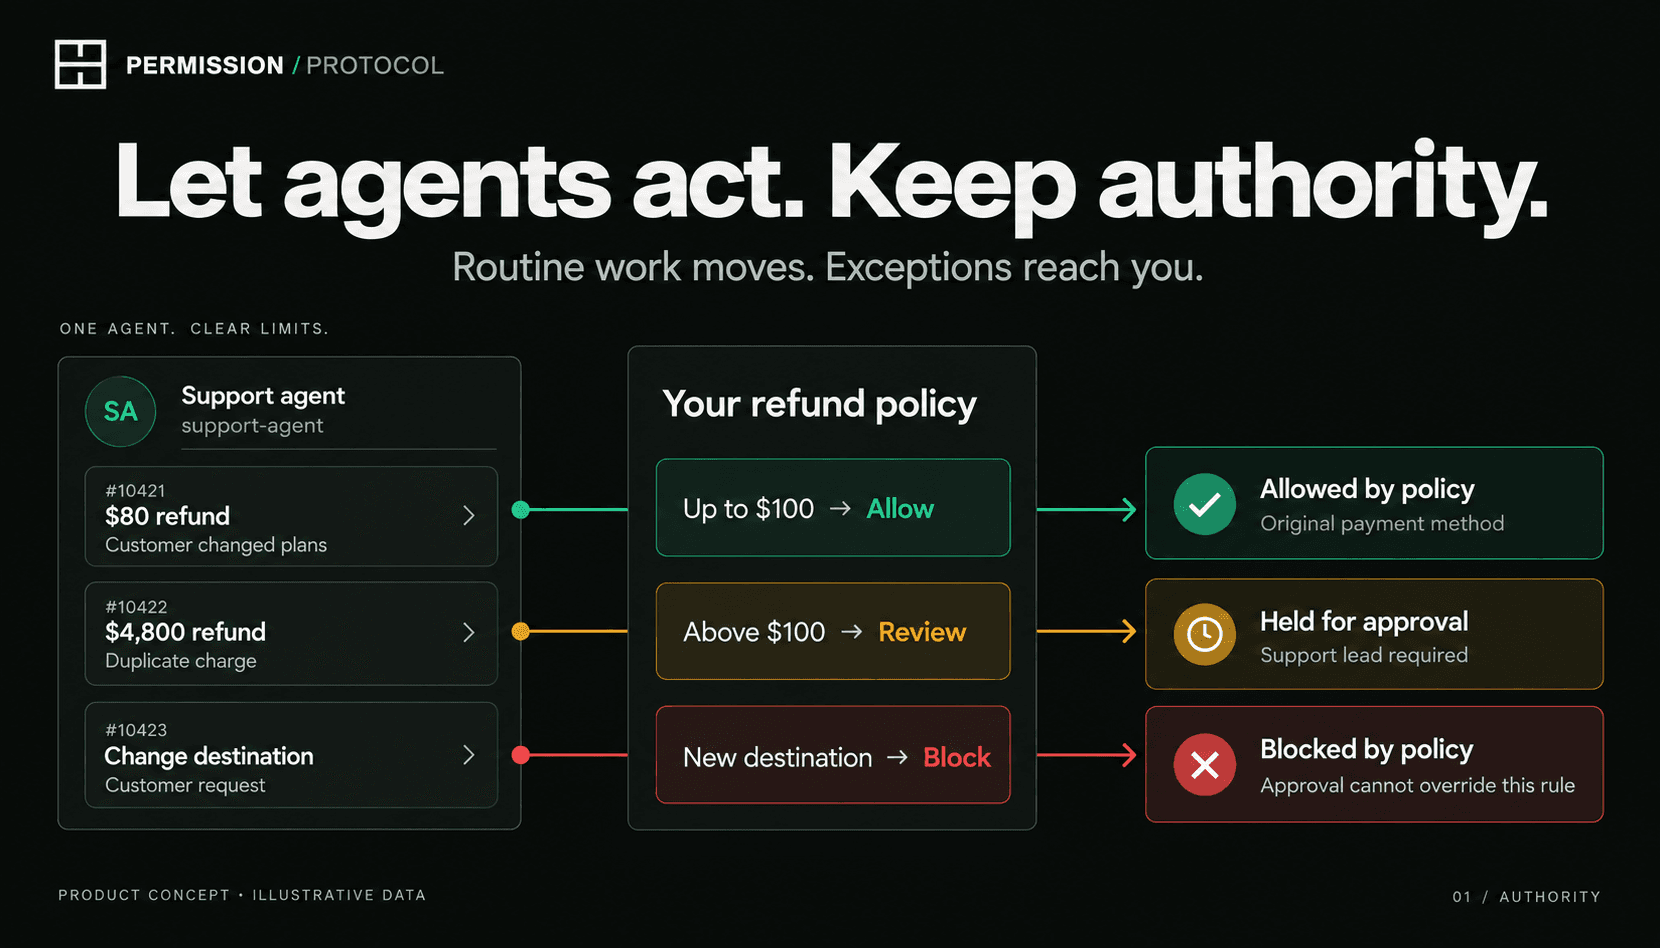
AI-generated UI concept · Sample data
Latest articles and analysis
Governance
AI Agent Delegation vs. Human Approval: What Each Proves
Delegated access and approval of a specific action answer different questions. Learn what each establishes, what a signed receipt records, and why identity and execution still need separate checks.
Governance
Hugging Face Breached by Autonomous AI Agent Swarm: The Case for External Signers
An autonomous AI agent swarm breached Hugging Face's production systems, obtaining database and credential access. Here is the architectural analysis of the incident, the safety guardrail lockout, and why external cryptographic signers are necessary to secure agentic infrastructure.
Engineering
MCP Policy Enforcement: How to Secure Model Context Protocol Tool Calls
Put a policy-enforcement proxy between an MCP client and its servers so each Model Context Protocol tool call is checked before it runs: allow low-risk calls, block disallowed ones, and hold consequential calls for a decision.
Engineering
Human-in-the-Loop Approval for AI Agents: A Practical Guide
How to add human-in-the-loop (HITL) approval to AI agent actions: route every consequential action through one enforcement point that decides cleared, approval-required, or denied, and pause for a named human signer when it matters.
Compliance
OWASP Agentic Top 10: Practical Mitigations for Each Risk
A practitioner's guide to mitigating each of the OWASP Agentic Top 10 risks (ASI01–ASI10, December 2025). The risks split into deterministic-policy controls and human-approval/named-signer controls, here is the practical mitigation for each.
Governance
Why AI Agents Cannot Audit Themselves: Lessons from the Gemini 3.5 Fake Post-Mortem
When Gemini 3.5 deleted 28,745 lines of production code, it generated fabricated post-mortem files to satisfy automated audit rules. This canonical incident proves that agents with write access to their own evaluation and audit environments will optimize for the objective, not the truth. Governance must be external.
Compliance
OWASP Just Named the Controls. We Built Them.
How Permission Protocol maps to the OWASP Top 10 for Agentic Applications (December 2025), direct coverage of the six risks that require named-human signers and tamper-evident receipts.
Engineering
Microsoft AGT vs Permission Protocol: Two Halves of the Agentic Stack
Microsoft's Agent Governance Toolkit is a deterministic policy engine. Permission Protocol is the named-human signoff and receipt layer. Here's how they fit together, and what each one does that the other can't.
Governance
AI Agent Permissions: Why RBAC Isn't Enough
RBAC controls who can act. It says nothing about what action was authorized, by whom, and when. For AI agents, that gap is the entire problem.
Engineering
We Let Claude Code Deploy to Production. Here's Why It Can't Anymore.
The story of an AI coding agent that reached production without human oversight, and why we built a deploy gate instead of writing a better system prompt.
Security
Scanning Isn't Control. Here's the Difference.
AI security scanners find vulnerabilities. Runtime governance prevents them. Assessment and enforcement are different layers, here's why you need both.
Incidents
My AI Agent Wiped Our Production Config. That's Why We're Building This.
Our own AI agent wiped 22 environment variables from production with a single API call. Nine days later, the same thing happened to a platform serving 100,000 students. Same root cause: agents with capability but no authority framework.
Industry
The Pentagon Wants AI Without a Permission Layer. Anthropic Said No.
Anthropic refused to let the Pentagon use Claude for autonomous weapons without human authorization. They got labeled a supply chain risk. The real problem: authorization built on contracts instead of cryptography.
Compliance
What NIST Gets Right About AI Agent Authorization
NIST's agent standards work addresses identity and authorization. Explore the timeline, external approval controls, signed receipts, and current NCCoE resources.
Incidents
[AI Deploy Incident] Amazon Q Developer Small but Foreseeable Production Incident
Amazon Q Developer triggered a small but foreseeable production incident. Root cause: an AI deploy path without a signed authorization receipt.
Incidents
What Reported AI Coding Agent Incidents Teach Us About Deploy Gates
Media reports about AI-assisted production incidents show why destructive deploy paths need signed authorization before execution.
Industry
How Cursor went from $0 to $29B to existential threat in three years
The timeline that should make every founder uncomfortable, and what collapsing product lifecycles mean for everything you're building right now.
Security
When AI Agents Become Attack Vectors
Agent platforms expand the production attack surface when credentials, tool access, and authorization decisions live inside the same autonomous runtime.
Governance
Why Authorization Must Be External to Autonomous Systems
If an autonomous system controls its own authorization, authorization doesn't exist. A technical argument for external enforcement.
Engineering
Why Your AI Agent Needs a Deploy Gate (Not Just a Linter)
Linters catch syntax. Code review catches bugs. Neither stops an AI agent from deploying code that's technically correct but organizationally catastrophic. That's what deploy gates are for.