Engineering
Human-in-the-Loop Approval for AI Agents: A Practical Guide
The takeaway
How to add human-in-the-loop (HITL) approval to AI agent actions: route every consequential action through one enforcement point that decides cleared, approval-required, or denied, and pause for a named human signer when it matters.
In this article
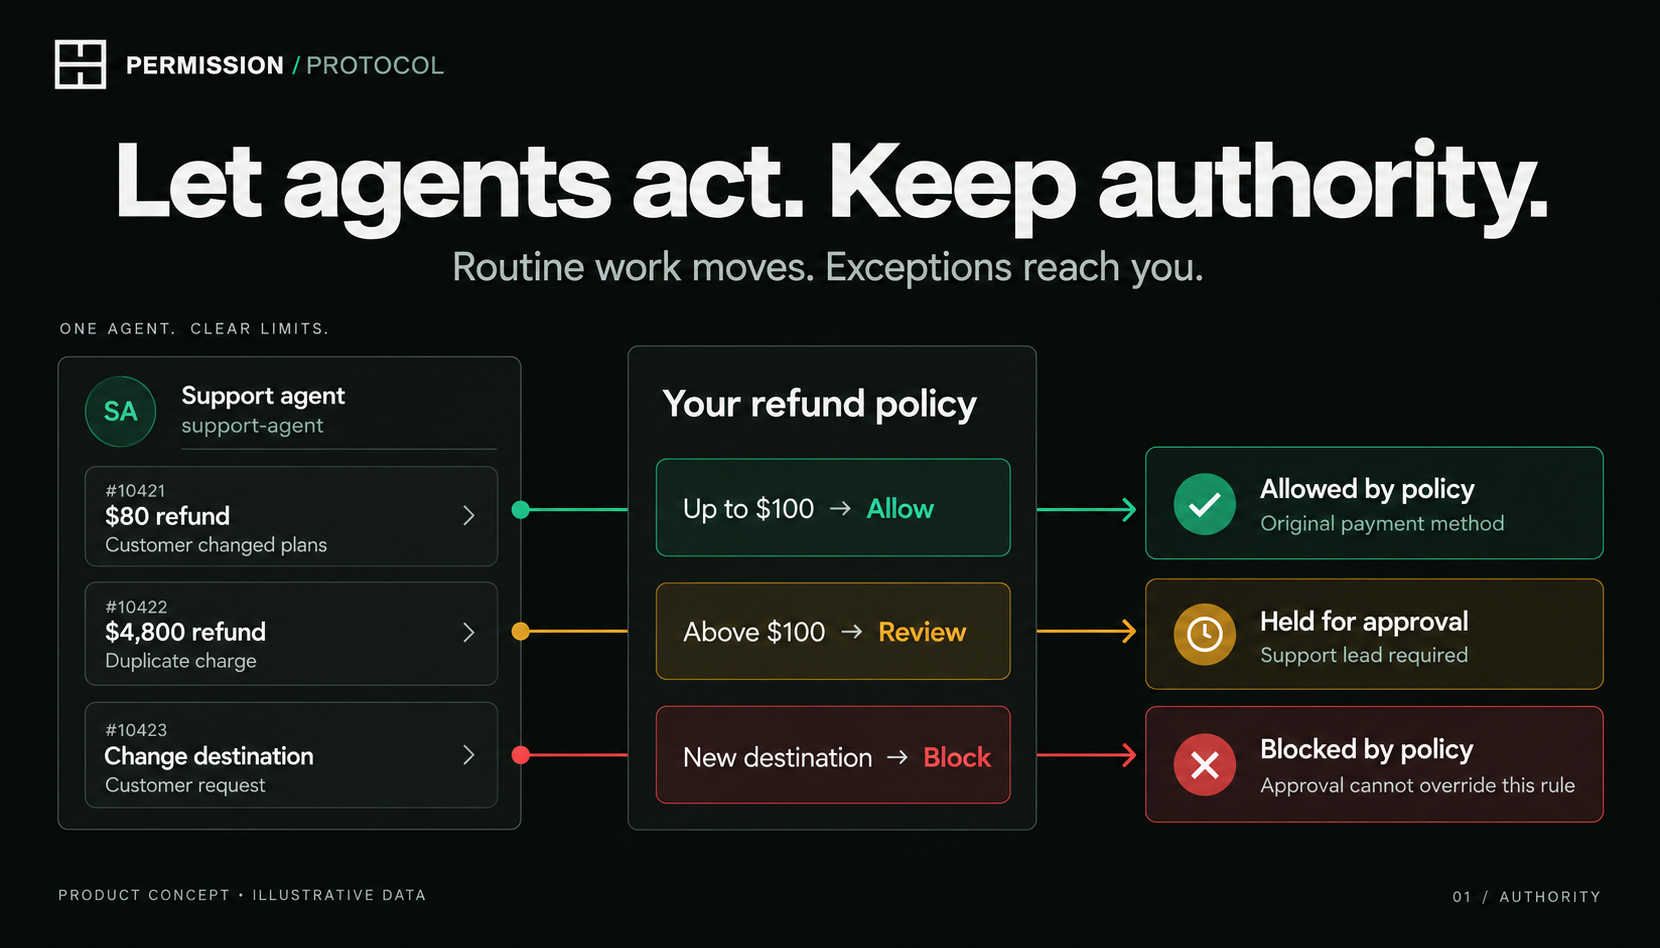
To add human-in-the-loop (HITL) approval to AI agent actions, route every consequential action through a single enforcement point that decides cleared, approval-required, or denied. When the decision is approval-required, the action pauses for a named human signer who approves it before it runs, producing an immutable receipt of who approved what. Below is how to wire it up.
Definition: what human-in-the-loop approval for AI agents is
Human-in-the-loop approval for AI agents is a control where consequential agent actions are routed through a single enforcement point that classifies each action as cleared, approval-required, or denied: and, when approval is required, pauses the action until a named human signer explicitly approves it before it runs. It turns “the agent decided it was fine” into “this specific person approved this specific action at this time, and here is the receipt.”
Why a confirmation prompt is not enough
The naïve way to add a human to the loop is a confirmation dialog: “Are you sure? [Yes] [No].” For an autonomous agent this is theater. The agent's own loop is the thing answering the prompt: there is no separation between the actor and the approver, so the agent can satisfy its own check. You need the decision to live at a point the agent does not control, with a real human at the other end of the consequential calls.
Simple confirmation prompt vs. policy-routed HITL approval
| Property | Simple confirmation prompt | Policy-routed HITL approval |
|---|---|---|
| Decides per-action risk | No, prompts the same way every time | Yes, engine classifies each action |
| Names who approved | No, just a click | Yes, a named human signer |
| Agent can self-satisfy | Yes, the agent's loop clicks through | No, decision is external to the agent |
| Produces an audit record | No durable artifact | Yes, immutable receipt |
| Scales to many actions | Poorly, every action interrupts | Yes, most auto-clear, only the risky slice escalates |
Choose where the approval check runs
The pattern is the same everywhere. What changes is where the action actually executes, because the check has to sit on that path. An approval recorded somewhere the action does not pass through does not stop it.
- A pull request merge or a production deploy: Deploy Gate for GitHub workflows. For a pull request that needs approval, the Permission Protocol GitHub App posts a check that stays pending until a signer approves, and your branch rules can require that check before merge. The approval is checked against the pull request's head commit, and Permission Protocol issues a signed receipt for it. Limit: It covers changes that go through the gated workflow. Commands run with direct cloud or database credentials are outside it.
- An MCP tool call: MCP Guard for tool calls. MCP Guard is an open-source stdio proxy that allows, blocks, or holds named tools before the server runs them. Limit: MCP Guard 0.1.0 records no approver identity and writes an unsigned local decision log, so it gives you a policy check, not the named-human record described above.
- Another consequential action, such as a refund or a data change: Walk through an approval. Follow one request through approval, denial, and the resulting record. Limit: The walkthrough is an illustration: nothing real runs, and no approval or receipt is created.
- Proving later who approved an action: How to read an authorization receipt. An authorization receipt records the action, the approver, the policy, and the time, signed so it can be checked outside the system that ran the action. Limit: A receipt shows who approved what. It does not show that the action was safe or that it ran successfully.
Each option covers only the actions routed through it. Human approval on its own does not make an agent safe or a system compliant: it gives you a decision point and a record for the actions you route through it.
Set it up in four steps
If your workflow uses LangGraph, start with its native interrupt and checkpoint APIs. Our LangGraph approval tutorial includes runnable approval and rejection paths, a process restart, and measured retry behavior. The example uses a mocked action and does not require a Permission Protocol integration.
These steps use Permission Protocol's Permission Router, but the pattern is general: one enforcement choke point, a per-action decision, a named human on the escalations, and a durable record.
- Wrap the agent's tool calls behind one enforcement call. Instead of calling tools directly, route every consequential action through a single choke point, Permission Protocol's Permission Router (
POST /api/v1/execute). It is receipt-first: a receipt is created before any tool executes. - Let the engine classify. The Consequence Engine predicts a decision for each action:
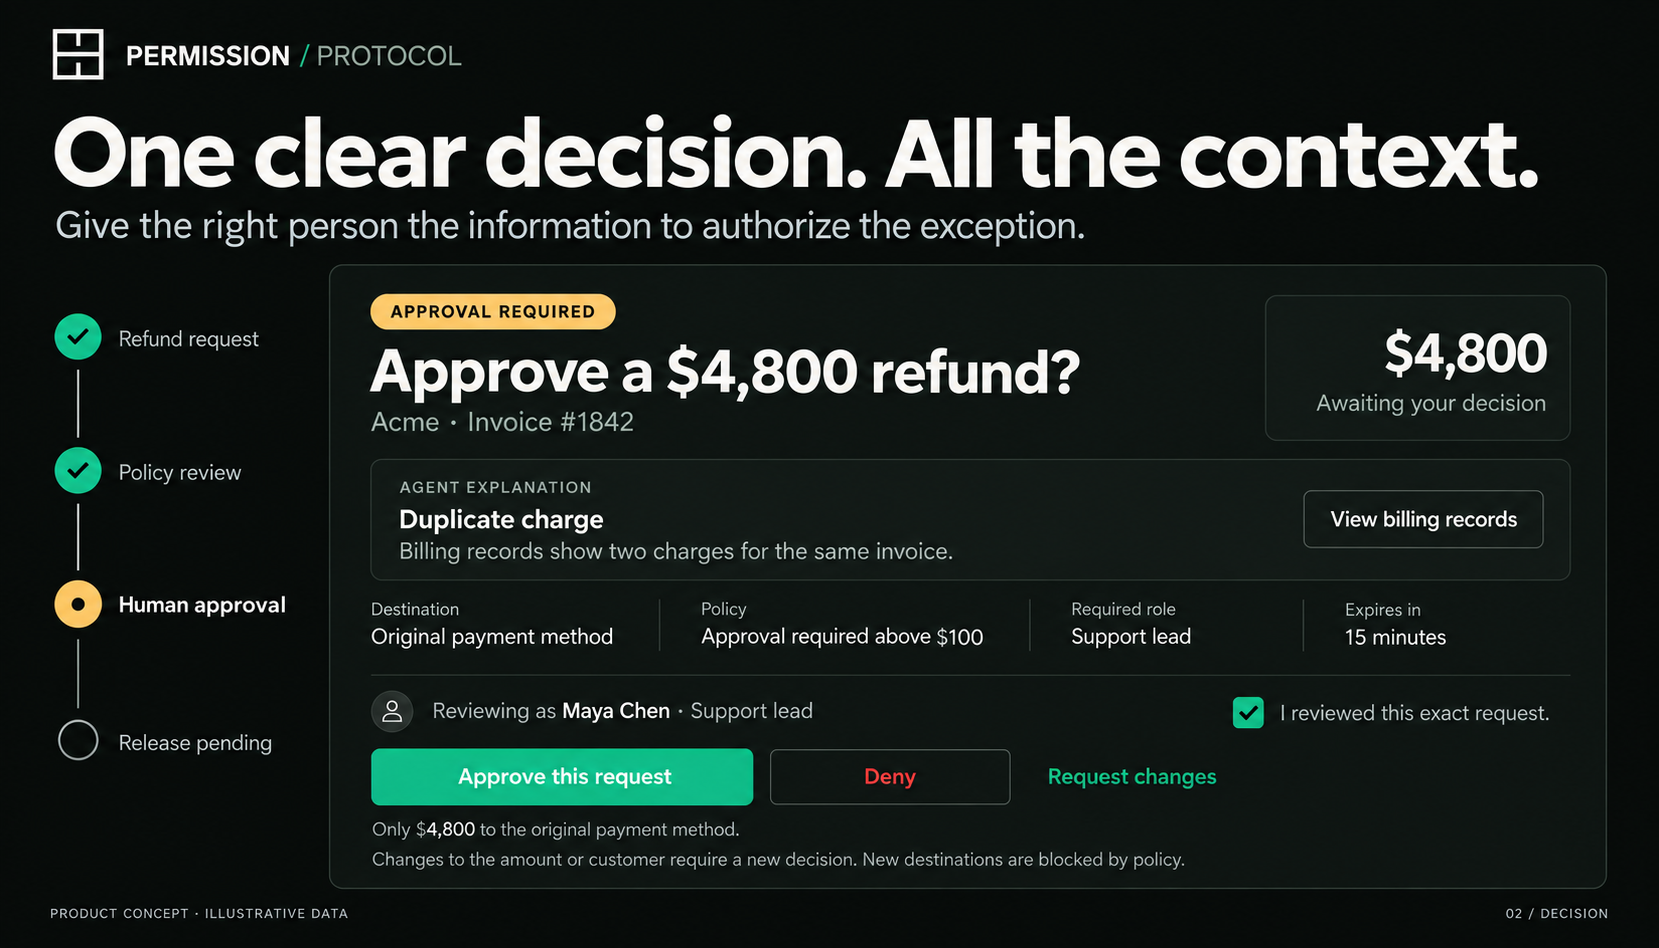
clearedauto-runs with no human in the path,approval_requiredpauses the action, anddeniedstops it outright. - A named human signs. When an action is approval-required, it routes to a specific human signer who reviews it and approves, the action proceeds only then. The agent cannot stand in for the signer.
- The receipt records it. Each approval is captured as an immutable receipt (signer, action, decision, timestamp) that you can export to your evidence vault. See how to read an authorization receipt.
Two properties make this trustworthy: the decision lives at a point the agent does not control, and the receipt exists before any tool runs, so authorization is never reconstructed after the fact.
Common mistakes
- Confirmation dialogs the agent can click through. If the same loop that proposes the action also answers the prompt, you have no human in the loop. The decision must be external to the agent.
- Approving by role, not by named person. “An approver approved it” is not an answer an auditor accepts. Route to a named human signer and record who they are.
- Gating everything. Pausing on every action kills throughput and trains people to rubber-stamp. Only escalate the slice that actually needs it, let the rest auto-clear.
- No durable record. An approval that leaves no exportable artifact will not satisfy an auditor. Keep the receipt.
For the pull-request-specific version of this pattern, see why an AI coding agent needs a deploy gate. And to see how a deterministic policy engine and named-human signoff fit together, read Microsoft AGT vs Permission Protocol.
Frequently asked questions
What is human-in-the-loop approval for AI agents?
Human-in-the-loop (HITL) approval for AI agents is a control where consequential agent actions are routed through a single enforcement point that classifies each action as cleared, approval-required, or denied: and, when approval is required, pauses the action until a named human signer explicitly approves it before it runs. The decision is recorded as an immutable receipt, so you always know who authorized what and when.
How is HITL approval different from a confirmation prompt?
A confirmation prompt is a dialog the calling code presents, and an autonomous agent's own loop can simply click through it: there is no separation between the actor and the approver. Policy-routed HITL approval moves the decision to an external enforcement point the agent does not control: the engine decides per-action risk, escalation goes to a named human (not a role the agent can satisfy), and every approval produces a durable, exportable record.
Does requiring human approval slow agents down?
No. Most actions auto-clear and run with no human in the path. Only the consequential slice, the actions classified as approval-required, pauses for a named signer. Because the enforcement point gates the few actions that matter instead of every call, throughput stays high while the risky actions still get an explicit human decision.
Last updated: October 14, 2026. Permission Protocol is the external authorization layer for AI agent actions, per-action human approval and tamper-evident receipts. See the OWASP Agentic Top 10 mapping for the full control coverage.
Put it into practice
Inspect an example receipt
Inspect a published authorization record, its scope and its verification details.