Skip to content
PERMISSION/PROTOCOL

Your agent is ready to act.Someone has to sign for it.

Policy clears the routine.A named human signs the consequential.Each one leaves a signed receipt.

npx -y @permission-protocol/[email protected] --config pp.config.yaml --mode observe -- node my-mcp-server.js

Free and open source: MCP Guard's observe mode logs each decision (setup guide). Deploy and MCP gates ship today; other gates go live with you as a First Gate.

Agent requests

1 cleared · 3 waiting

Pick one to try it below

When it stops being optional

You need a signature the week one of these happens.

  1. A customer security review asks who approves agent actions.

    Security questionnaire

    AI-07 Who approves agent actions?

    A named owner signs each consequential action. Evidence: rcpt_dg_cmt3…8pk5

    A coding agent uploaded customers' repositories without consent.
  2. An agent is about to move money or export data.

  3. An auditor asks for evidence.

    Terminal

    $ npx @permission-protocol/verify \
      artifact.json --keys keys.json
    ...
    Signed decision: APPROVED
    Decider: rodchalski
    Commit: a2df259d
    VERIFIED: rcpt_dg_cmt3gkieg0003v5cwonna8pk5
    
    A developer says Gemini deleted 28,745 lines of code and fabricated the post-mortem.

Try the gate.

Example

1 · Agent asks

2 · Gate decides

Needs a signature

Refund $4,800.00

cx-refunds · charge ch_3Nq8

Policy · pp.config.yaml

- id: hold-refund
  tool: issue_refund
  action: require_approval
Maya OkaforFinance approver

3 · Receipt

No receipt yet

Waiting for Maya Okafor.

Not executed

For engineering and review teams

Keep your approvals. Make them evidence.

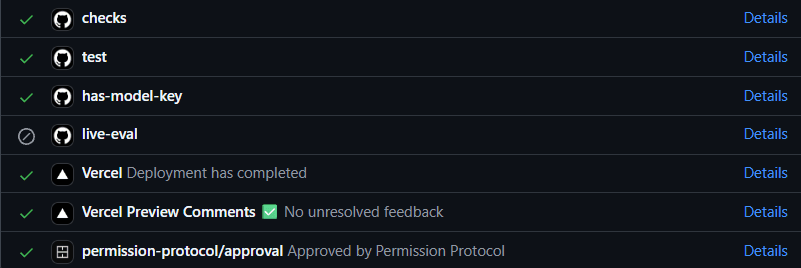
Checks on pull request #735 to this site after merge, all passed: checks passed, test passed, has-model-key passed, live-eval skipped, Vercel deployment completed, Vercel Preview Comments with no unresolved feedback, and permission-protocol/approval passed with the status "Approved by Permission Protocol". The permission-protocol/approval row is highlighted.
A real pull request to this site.

It's one more required check, not a new review tool. Your code reviews and CI stay as they are. Each merged change gets a signed receipt naming who authorized it.

See the receipt for this pull request

Emergency stop: one button closes every connected gate. How it works

Proof

What a signature looks like, and what happens without one.

Our own deploy, signed.

Permission Protocol issued this receipt when this site's own deploy was approved, and its signature was checked against the published key when this page was built. To check a receipt yourself, export its full artifact and run the open-source verifier:

npx @permission-protocol/verify artifact.json --keys keys.json
Inspect the signed receipt

✓ ACTION AUTHORIZED

github-actions → production

Deploy gate authorization approved

Agent
github-actions
Signer of record
rodchalski
Policy
deploy-gate-v1
Timestamp
2026-08-21T22:26:38.587Z
SignatureVerified ✓

Ed25519 signature verified at build time over the canonical payload digest against the issuer public key published at /api/v1/keys/current

Issuerpermissionprotocol.com
Technical Details

Key ID

pp_key_348f56d61d0deab4

Key fingerprint

SHA256:Is7fInHqiSzzPaHqEJeJUMG/L7MEMs0zYT3R8g95z3s

Payload digest (sha256)

aa4729afd171817a690ab21ae46e16888a854a20c4096f778bc1e6ccbdaccc69

Signed payload bytes (base64)

eyJhZ2VudElkIjoiZ2l0aHViLWFjdGlvbnMiLCJhdHRyaWJ1dGlvbkNvbmZpZGVuY2UiOiJjcmVkZW50aWFsZWQiLCJjYW5vbmljYWxpemF0aW9uIjoiamNzX3YyIiwiY29tcGFueUlkIjoiY21sazMxbGw4MDAwMXppbGJqcGpyOGt5bCIsImNyZWF0ZWRBdCI6IjIwMjYtMDgtMjFUMjI6MjY6MzguNTg3WiIsImRlY2lkZXJBdXRoTWV0aG9kIjoic2Vzc2lvbiIsImRlY2lkZXJEaXNwbGF5Ijoicm9kY2hhbHNraSIsImRlY2lkZXJJZCI6InVzZXI6Y21rcmM2ZmliMDAwMDkwY2p3dnZyc3RscSIsImV4cGlyZXNBdCI6IjIwMjYtMDgtMjFUMjI6NDE6MzguNTY1WiIsImlkIjoicmNwdF9kZ19jbXQzZ2tpZWcwMDAzdjVjd29ubmE4cGs1IiwiaWRlbUtleSI6ImRlcGxveS1nYXRlOmNtdDNna2llZzAwMDN2NWN3b25uYThwazU6NmUyNzg0NmZlM2YyMjRjOWZjYTdiNWQ3ODNhYWM1MTllYjM1ZWEzOTJlMTJhNzI3MTEzNzQ3NzJmZWRhYzBjNiIsImlucHV0SGFzaCI6IjZlMjc4NDZmZTNmMjI0YzlmY2E3YjVkNzgzYWFjNTE5ZWIzNWVhMzkyZTEyYTcyNzExMzc0NzcyZmVkYWMwYzYiLCJwb2xpY3lWZXJzaW9uIjoiZGVwbG95LWdhdGUtdjEiLCJyZWFzb25Db2RlcyI6IltcIkRFUExPWV9HQVRFX0FQUFJPVkVEXCJdIiwicmVjZWlwdFZlcnNpb24iOjIsInJlcXVlc3RKc29uIjoie1wiYWN0aW9uXCI6e1wib3BlcmF0aW9uXCI6XCJkZXBsb3lcIixcInRvb2xcIjpcImdpdGh1Yi1hY3Rpb25zXCJ9LFwiY29udGV4dFwiOntcImVudmlyb25tZW50XCI6XCJwcm9kdWN0aW9uXCIsXCJyZXZlcnNpYmlsaXR5XCI6XCJSRVZFUlNJQkxFXCJ9LFwiZW5yaWNobWVudFNuYXBzaG90XCI6e1wiY29uZmlkZW5jZVdhcm5pbmdzXCI6W1wiTGFyZ2UgY2hhbmdlc2V0IOKAlCBzdW1tYXJ5IG1heSBub3QgY2FwdHVyZSBhbGwgY2hhbmdlc1wiXSxcImdlbmVyYXRlZEF0XCI6XCIyMDI2LTA4LTIxVDIxOjI1OjUxLjUzMlpcIixcImxpbmtlZElzc3VlVGl0bGVcIjpudWxsLFwicmlza1NpZ25hbHNcIjpbXSxcInN1bW1hcnlcIjpcIlRoaXMgcHVsbCByZXF1ZXN0IGNoYW5nZXMgcHJvZHVjdCBvciBkZXBsb3kgYmVoYXZpb3IgaW4gdGhlIGFyZWFzIGRlc2NyaWJlZCBieSB0aGUgZW5naW5lZXJpbmcgdGVhbS4gUmV2aWV3ZXJzIG1heSBzZWUgYSBkaWZmZXJlbnQgcmVzdWx0IGluIHRoZSBhZmZlY3RlZCB3b3JrZmxvdyBhZnRlciB0aGlzIGlzIHJlbGVhc2VkLiBPcGVyYXRvcnMgbWF5IG5lZWQgdG8gd2F0Y2ggdGhlIGFmZmVjdGVkIGZsb3cgY2xvc2VseSBvbiB0aGUgZmlyc3QgZGVwbG95LlwiLFwidmVyaWZpY2F0aW9uU3RlcHNcIjpbXX0sXCJpbnRlbnRcIjp7XCJjYXRlZ29yeVwiOlwiZGVwbG95bWVudFwiLFwibmFtZVwiOlwiZGVwbG95X2dhdGVfYXBwcm92YWxcIixcInN1bW1hcnlcIjpcIkRlcGxveSBnYXRlIGF1dGhvcml6YXRpb24gYXBwcm92ZWRcIn0sXCJtZXRhZGF0YVwiOntcImRlcGxveUdhdGVSZXF1ZXN0SWRcIjpcImNtdDNna2llZzAwMDN2NWN3b25uYThwazVcIn0sXCJwb2xpY3lcIjp7XCJleHBpcmVzQXRcIjpcIjIwMjYtMDgtMjFUMjI6NDE6MzguNTY1WlwifSxcInNjb3BlXCI6e1wiYXJ0aWZhY3RfZGlnZXN0XCI6bnVsbCxcImNhcGFiaWxpdHlcIjpcImRlcGxveTpwcm9kdWN0aW9uXCIsXCJjb21taXRTaGFcIjpcImEyZGYyNTlkMmM4NjUxYjI2ZDk5MWJiMzlmNzUwZjhiMjVlOGZkNjBcIixcImVudlwiOlwicHJvZHVjdGlvblwiLFwicmVmXCI6XCJyZWZzL3B1bGwvNTE5L2hlYWRcIixcInJlcG9cIjpcInBlcm1pc3Npb24tcHJvdG9jb2wvc2l0ZVwiLFwid29ya2Zsb3dcIjpudWxsfX0iLCJyZXNvbHV0aW9uVHlwZSI6ImFsbG93X29uY2UiLCJzY29wZSI6InByb2R1Y3Rpb24iLCJzaWduYXR1cmVBbGciOiJlZDI1NTE5Iiwic2lnbmF0dXJlS2V5SWQiOiJwcF9rZXlfMzQ4ZjU2ZDYxZDBkZWFiNCIsInN0YXR1cyI6IkFQUFJPVkVEIiwic3VtbWFyeSI6IkRlcGxveSBnYXRlIGF1dGhvcml6YXRpb24gYXBwcm92ZWQifQ==

Signature (base64)

h3v1UqFVSeS68d3uPTTQj0LQxs4Olqr4Mnn0wesA0kRiSekHSEKVM0rx5U8xLdq9IP8n4nh7xUva7bdUWNwzDg==

Verify it yourself

curl -so payload.bin https://permissionprotocol.com/homepage-receipt/payload
curl -so payload.sig https://permissionprotocol.com/homepage-receipt/signature
curl -so issuer.pem https://permissionprotocol.com/homepage-receipt/issuer-key
openssl pkeyutl -verify -rawin -pubin -inkey issuer.pem -in payload.bin -sigfile payload.sig

The shared receipt page shows a redacted view; the full verifiable artifact is above.

app.permissionprotocol.com/r/rcpt_dg_cmt3gkieg0003v5cwonna8pk5

Two incidents. No one signed for either of them.

From the AI Agent Incident Tracker we maintain. Each record links its sources.

AI Agent Incident Tracker

239 sourced records · 110 realized · 129 demonstrated

  • Security review

    A coding agent uploaded customers' repositories without consent.

    Gate: holds the upload for a data owner.

    · Media report

    Read the record
  • Audit evidence

    A developer says Gemini deleted 28,745 lines of code and fabricated the post-mortem.

    Gate: holds the deletion and keeps the receipt.

    · Media report

    Read the record

Records can overlap. Counts describe this collection, not the frequency of agent failures. Methodology · Snapshot 2026-11-10

Explore all 239 incidents

Start

Install it free today, or have us put your first gate live.

First Gate

One gate live in 30 days, or a full refund.

$10,000 introductory price for the first 5 customers

  • Your action, your engineer, a founder on every call.
  • Starts in observe mode. Nothing is blocked until you turn enforcement on.
  • Acceptance criteria agreed on day one. Miss them and the fee is refunded in full.

20-minute call. No commitment. Nothing auto-renews.